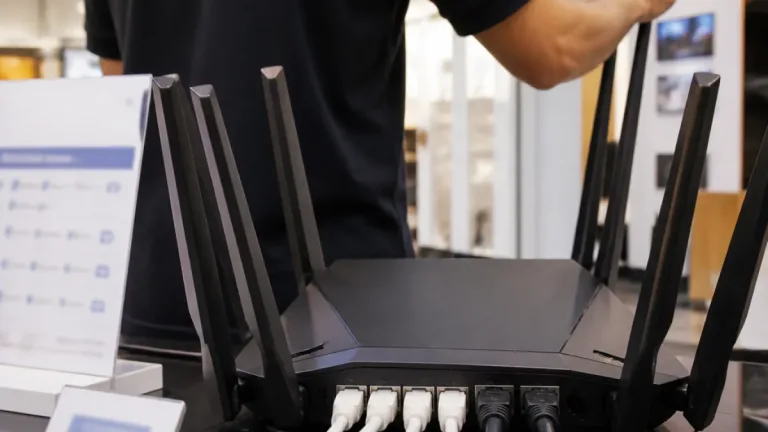
Standard: A 16-year-old vulnerability in Broadcom’s implementation of Wi-Fi Protected Setup (WPS) can be triggered remotely by an attacker within radio range to execute commands with root privileges on affected networking devices, according to published research and a public demonstration.
Speed claim: Security researcher Quentin Kaiser used artificial intelligence (OpenAI’s Codex) to accelerate discovery and produced proof-of-concept exploit code in weeks, culminating in a live demonstration at the Hexacon conference in Paris and public disclosure on October 15, 2026.
Real-world caveat: The proof of concept exploited specific ISP gateway firmware — notably a Sagemcom-built BBOX3V+ used by Proximus — and by the date the vulnerability became public, affected devices remained unpatched, according to the researcher’s timeline. The advisory and details name Broadcom’s WPS implementation as the root cause; Broadcom attempted a patch in 2018 but the issue persists in some deployed devices.
What the vulnerability is and how it was demonstrated
The flaw, dubbed WPSplinter by the reporting researcher, stems from a memory-handling error introduced in 2010 that can cause a device to combine more data than available memory allows. That overflow can enable an attacker to overwrite device memory regions, potentially allowing data exfiltration, remote code execution or device takeover without knowing the network password or completing normal WPS enrollment.
In a published demonstration at Hexacon, the researcher targeted Belgian internet service providers Proximus and Orange. Against one Proximus gateway, the researcher reported that exploit activity “opened a reverse shell, a remote command line, carried over Wi-Fi frames, so no outside server was needed,” and that work on the vulnerability used AI to shorten development time.
“Against a Proximus gateway, the Sagemcom-built BBOX3V+, the exploit opened a reverse shell, a remote command line, carried over Wi-Fi frames, so no outside server was needed,” the researcher wrote.
Disclosure timeline and vendor response
- Vulnerability introduced in 2010 in Broadcom’s WPS codebase.
- Broadcom attempted to patch the issue in 2018.
- Researcher Quentin Kaiser reported the bug on July 18 and again on July 27, 2026, initiating a 90-day disclosure window.
- The vulnerability was made public on October 15, 2026; as of that date the researcher said none of the affected networking devices had been patched.
The researcher also noted using OpenAI’s Codex to assist in identifying and exploiting the issue, saying the AI reduced time and cost compared with traditional manual analysis.
What the extracted text names and what it does not
The reporting identifies Broadcom’s WPS implementation as the vulnerable component and documents a working exploit against a Sagemcom BBOX3V+ gateway deployed by Proximus; the researcher also exercised proof-of-concept activity against devices on Orange networks. The published material explains the bug allows remote triggering from radio range and does not require the router password or normal WPS enrollment.
| item | detail |
|---|---|
| vulnerability name | WPSplinter |
| affected component | Broadcom Wi-Fi Protected Setup (WPS) implementation |
| first introduced | 2010 |
| researcher | Quentin Kaiser |
| public disclosure | October 15, 2026 |
What installers and integrators should note from the report
- The flaw targets a legacy component (WPS) still present in many devices; the exploit can be triggered from radio range without authentication.
- The researcher’s disclosure timeline shows responsible reporting occurred in July 2026 with public details released after the 90-day window in October 2026.
- The published demonstration includes an ISP gateway model (Sagemcom BBOX3V+) that the researcher successfully compromised as a proof of concept.
This report provides technical and timeline details that integrators, managed-service teams and security specialists can use to check installed equipment inventories and coordinate with vendors or ISPs on patches and firmware updates. Installers should therefore seek vendor advisories and confirmed firmware updates before assuming a given device is fixed.